
Governance, Risk & Compliance
getTRAC
Compliance automation and governance platform
1 min readLast reviewed July 18, 2026
The Problem
Why getTRAC exists
Compliance evidence usually lives in scattered spreadsheets, screenshots, and email threads — rebuilt from scratch every audit cycle, by whoever drew the short straw. It gets harder still the moment a business operates across more than one regulatory region.
Industry Pain Points
What most teams are stuck with today
- Evidence collection is a multi-week scramble before every audit
- The same control gets manually re-verified for every framework it touches, with no shared source of truth
- Ownership of individual controls is unclear, so gaps sit unnoticed until an auditor finds them
- Businesses operating across India, the Middle East, and Southeast Asia end up running a separate compliance tool per region instead of one control set mapped to all of them
How Threat ResQ Solves It
Inside getTRAC
getTRAC continuously monitors controls against every framework you're scoped for — global or regional — automatically collects the evidence auditors ask for, and assigns clear ownership, so the audit becomes a formality, not a fire drill, no matter which regulator you answer to.
getTRAC — Live Overview
Readiness Trend
55%
See It In Action
getTRAC, up close
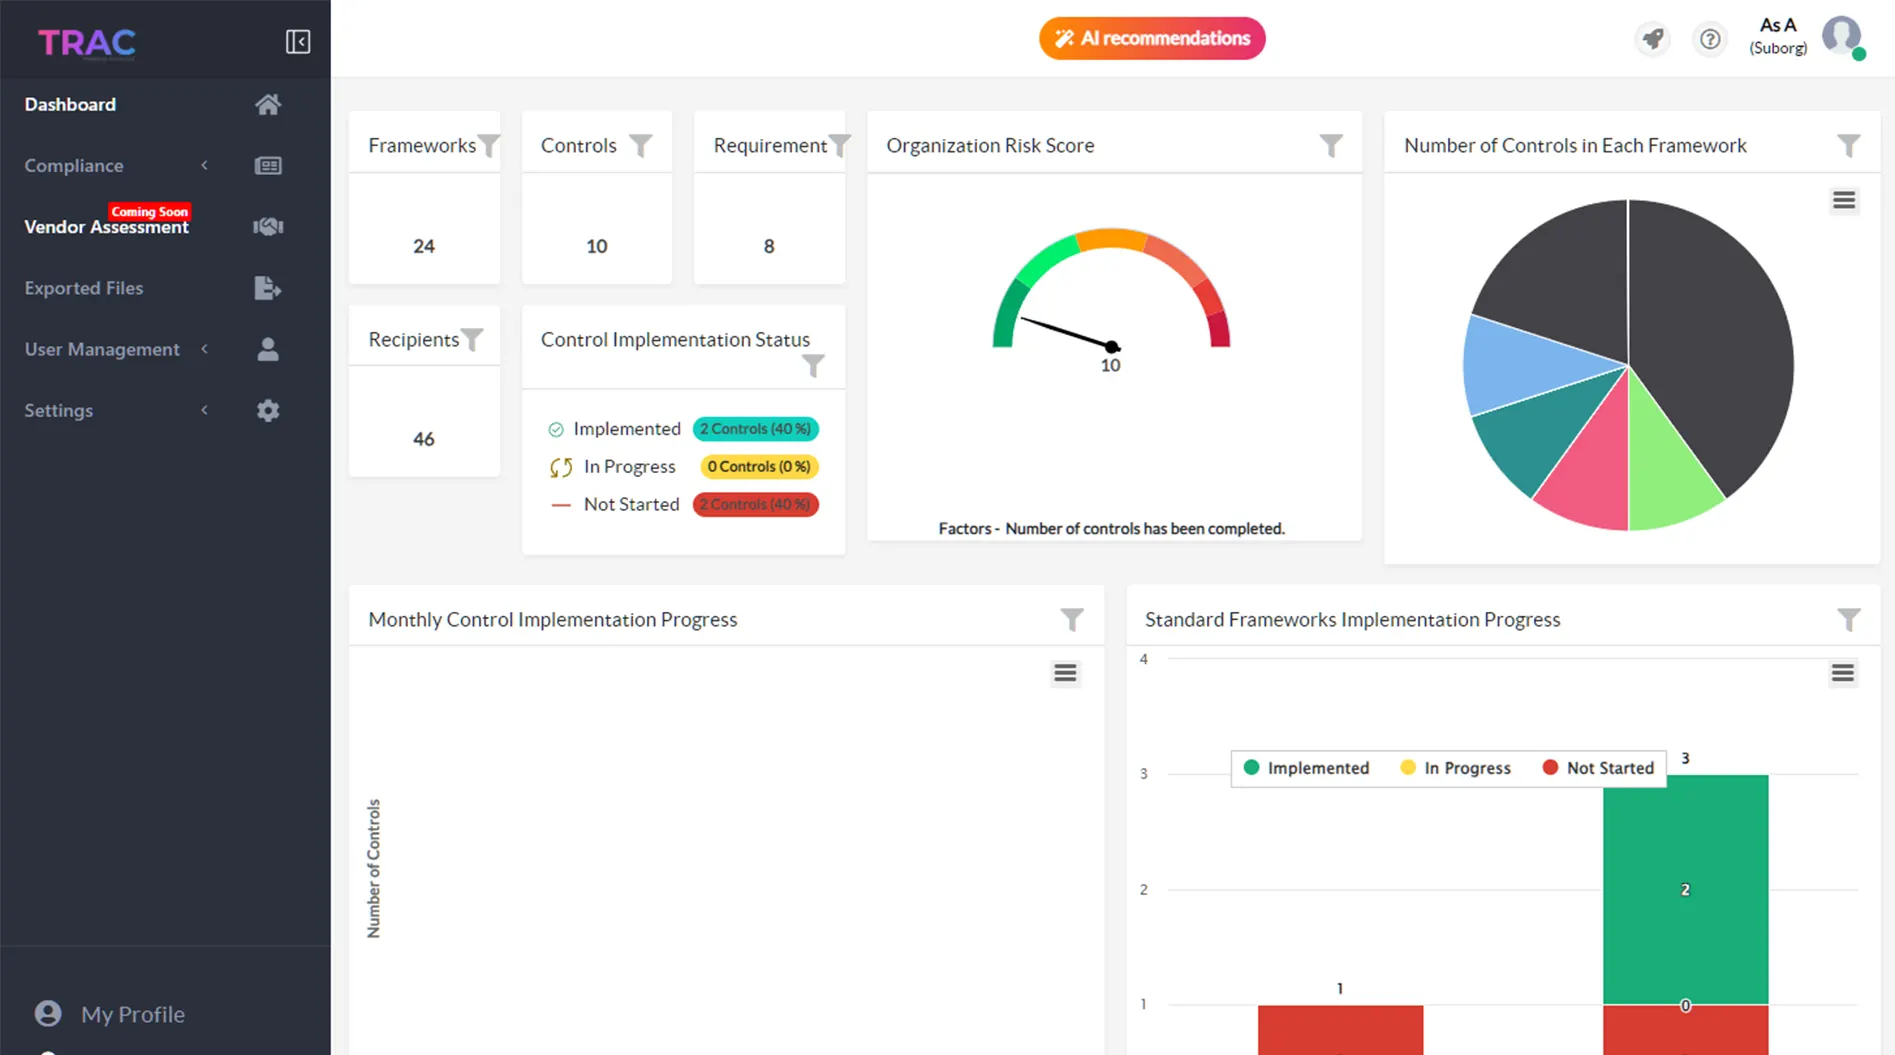
getTRAC — Detail / drill-down view
Screenshot placeholder
getTRAC — Reporting & export
Screenshot placeholder
Additional views coming soon.
Use Cases
Where teams put this to work
SOC 2 readiness
Map existing controls to SOC 2 and start collecting evidence months before the audit window opens.
Multi-framework enterprises
Map a control once, reuse the evidence across every framework it satisfies instead of re-verifying per certification.
Multi-region operations
Run one control set across India (RBI-CSF, SEBI, CERT-IN), the Middle East (NCA ECC, UAE ISR), and Southeast Asia (PDPA) instead of a separate compliance tool per region.
Vendor security questionnaires
Answer enterprise customer security questionnaires directly from a current, evidenced control set.
Business Outcomes
What changes after adopting it
55%
Faster audit completion reported across getTRAC deployments
20+
Global & regional compliance frameworks mapped from one control set
47%
Lower compliance operations cost reported by customers
Feature Comparison
What changes, concretely
Traditional approach
getTRAC
Evidence collection is a multi-week scramble before every audit
Continuous control monitoring across 20+ global and regional frameworks
The same control gets manually re-verified for every framework it touches, with no shared source of truth
Custom framework builder for sector-specific or hybrid compliance standards
Ownership of individual controls is unclear, so gaps sit unnoticed until an auditor finds them
Automated evidence collection
Businesses operating across India, the Middle East, and Southeast Asia end up running a separate compliance tool per region instead of one control set mapped to all of them
Cloud compliance scanning against 200+ CIS benchmarks
Industries Served
Where getTRAC fits
getTRAC keeps evidence current across RBI, PCI DSS, and SOC 2 simultaneously, replacing the quarterly evidence-gathering fire drill BFSI compliance teams otherwise run separately for each framework.
getTRAC maps HIPAA and ISO 27001 controls to clinical reality, generating audit-ready evidence without adding steps to a nurse's shift.
getTRAC turns ISO 27001 and NIST control mapping into a continuous evidence trail auditors and insurers can use, even where OT/IT convergence complicates a traditional audit scope.
getTRAC automates the continuous evidence collection SOC 2 and ISO 27001 auditors expect, so compliance doesn't become a quarterly fire drill between funding rounds and enterprise deals.
getTRAC keeps NIST and ISO 27001 evidence audit-ready against the public-accountability standards government agencies operate under, without assuming an enterprise-scale compliance team.
getTRAC's continuous evidence collection lets IT/ITES firms answer a client's SOC 2 or ISO 27001 due-diligence questionnaire in hours instead of weeks.
Integrations
Fits into what you already run
Pricing is scoped to your environment.
getTRAC is priced per organization size and scope — talk to us for a quote, not a generic tier.
Capabilities
What's included
- Continuous control monitoring across 20+ global and regional frameworks
- Custom framework builder for sector-specific or hybrid compliance standards
- Automated evidence collection
- Cloud compliance scanning against 200+ CIS benchmarks
- Audit-ready reporting on demand
- Governance workflow and ownership tracking
FAQ
Common questions
Which frameworks does getTRAC support?
20+ global and regional frameworks — including ISO 27001, SOC 2, GDPR, HIPAA, PCI DSS, and NIST CSF globally; RBI-CSF, SEBI, and CERT-IN for India; NCA ECC (Saudi Arabia) and UAE ISR for the Middle East; and PDPA for Singapore and Malaysia — with controls mapped once and reused across every framework they satisfy. A custom framework builder covers sector-specific or hybrid standards beyond that list.
Does getTRAC replace our auditor?
No — getTRAC prepares the evidence and control mapping your auditor needs, so the engagement itself is faster and less disruptive, not a replacement for independent attestation.
Can getTRAC handle compliance across multiple regions at once?
Yes — it's built for organizations operating across India, the Middle East, and Southeast Asia, mapping controls once and applying them against each region's specific frameworks instead of running a separate tool per jurisdiction.
See getTRAC on your own environment.
30 minutes, no scripted pitch.